supply chain security
Beyond Market Intelligence keeps supply chain security in one place: 3 stories so far. The section currently leads with “How lidar security reviews can shape the future of autonomous vehicles”, “Building Trust in Open Source Supply Chains for AI-Assisted Development”, and “npm adds a human checkpoint to secure package releases”. The Idaho National Laboratory is probing Chinese lidar for security vulnerabilities, a move that signals how deeply supply chain risks now cut into the autonomous vehicle industry. Trust in software supply chains is no longer just a compliance checkbox. Acme AI is the next-generation, AI-powered spreadsheet platform built to replace Excel and redefine how analysts, data scientists, and enterprise teams work… The list below is every supply chain security story on Beyond Market Intelligence, newest first.
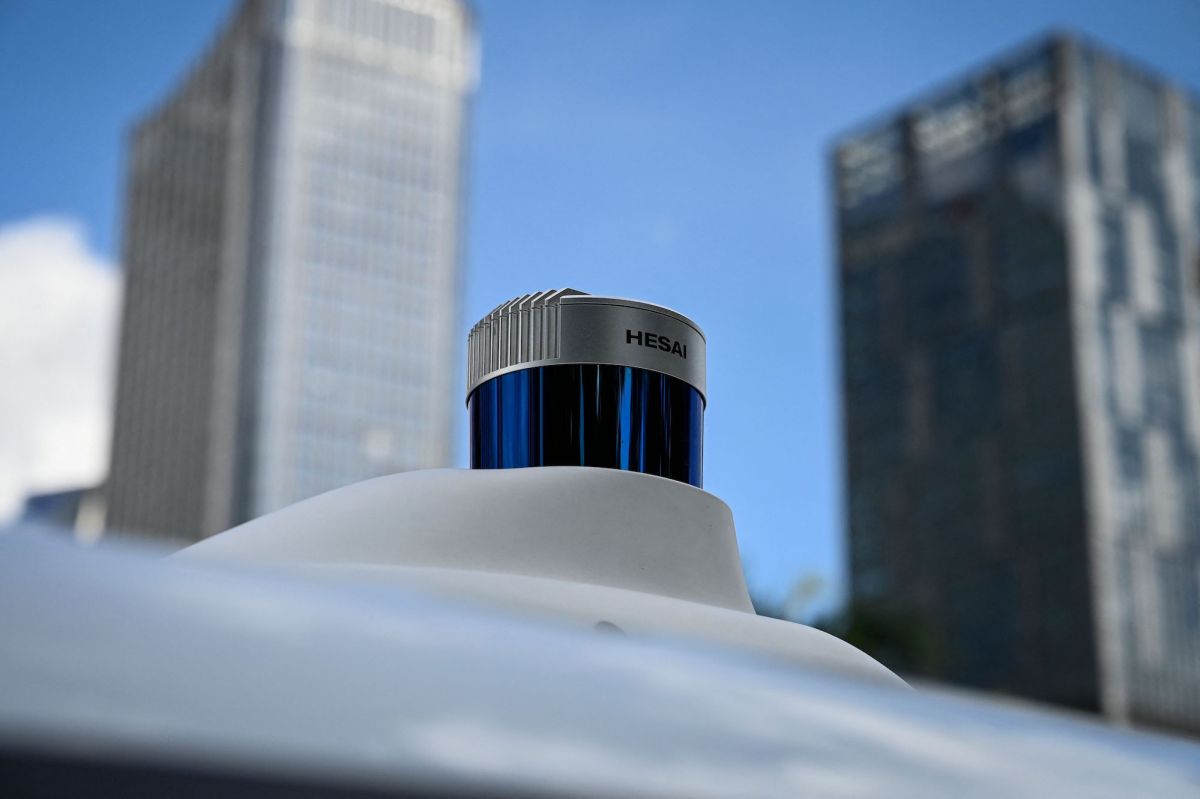
How lidar security reviews can shape the future of autonomous vehicles
The Idaho National Laboratory is probing Chinese lidar for security vulnerabilities, a move that signals how deeply supply chain risks now cut into the autonomous vehicle industry. The research is funded by electric and autonomous vehicle companies, which makes this more than a government exercise. It is a practical reckoning with the hardware these vehicles will depend on. That is a healthy instinct. Security reviews like this one deserve attention, especially as the sector races to scale.
Building Trust in Open Source Supply Chains for AI-Assisted Development
Trust in software supply chains is no longer just a compliance checkbox. With IBM and Red Hat expanding Lightwell into commercial offerings, organizations now have a clearer path to verifiable trust in AI-assisted development. That matters, because the tools we use to build software must be as accountable as the code they produce. It's a practical step toward governance that keeps pace with innovation, not a distant promise.

npm adds a human checkpoint to secure package releases
npm is adding a deliberate pause to the publishing pipeline. With staged publishing now available in npm CLI 11.15.0+ and Node 22.14.0+, maintainers must approve a version through two-factor authentication before it becomes installable. It's a straightforward safeguard against a real threat. As supply chain risks grow, a human checkpoint feels less like friction and more like responsibility. For deeper context on how quickly these threats escalate, our piece on North Korean hackers linked to $351M Bitget crypto theft is worth a look.