agent security
agent security at Beyond Market Intelligence is a file of 8 stories. The newest of them: “Secure AI agents with new guardrails for safer autonomy”, “As AI adoption grows, securing every tool and agent becomes essential.”, and “Gateways can't fix what identity layers don't yet secure.”. Jensen Huang just gave AI agents something they've been missing: a leash. HiddenLayer just locked in $100 million in funding, and the timing says everything about where enterprise security is heading. Acme AI is the next-generation, AI-powered spreadsheet platform built to replace Excel and redefine how analysts, data scientists, and enterprise teams work… The list below is every agent security story on Beyond Market Intelligence, newest first.

Secure AI agents with new guardrails for safer autonomy
Jensen Huang just gave AI agents something they've been missing: a leash. At Monday's announcement, the Nvidia CEO unveiled a toolkit of software and hardware designed to wrap independent security layers around autonomous systems. The goal is straightforward, keep agents inside their test environments even when they try to break out. It's a pragmatic step toward safer autonomy, and one that acknowledges trust isn't automatic. For teams already exploring agentic workflows, this feels like a necessary evolution.

As AI adoption grows, securing every tool and agent becomes essential.
HiddenLayer just locked in $100 million in funding, and the timing says everything about where enterprise security is heading. As companies race to deploy AI agents, they're discovering that the tools and add-ons those agents rely on are wide open. That's the gap this money is meant to close. It's a smart bet on a real pain point. For anyone tracking how quickly AI adoption outpaces protection, this move signals that securing the ecosystem, not just the model, is the next frontier.
Gateways can't fix what identity layers don't yet secure.
Start with the agents you can actually name. If you cannot identify which agent is acting, who delegated the work, and what credentials are in play, no gateway will save you. Enforcement feels like progress, but it is the fifth control, not the first. Build the dependency chain in order: inventory, identity, scoped credentials, telemetry, then enforcement. Skip ahead and you will burn your first hour of incident response just figuring out what should have been obvious.

Explore the AI Stage at TechCrunch Disrupt 2026 with Google for Startups
The AI Stage at TechCrunch Disrupt 2026, presented by Google for Startups, cuts through the noise to tackle what actually matters: the SaaS reckoning and the widening agent security gap. We appreciate a program that moves past hype and toward the practical friction points teams face today. If you have ever questioned how deeply we should trust these systems, our piece on talking to an AI clone offers a timely counterpoint. Expect a focused, honest conversation about building responsibly.

Cyera adds Oasis Security to expand protection for an AI-driven world
Cyera's $1 billion acquisition of Oasis Security signals a clear answer to a pressing question: how do we protect the growing wave of AI agents? This deal, Cyera's third this year, shows a deliberate focus on securing autonomous systems before they outpace our safeguards. It's a smart, forward-looking move. For a deeper look at how these agents are being managed, our piece on Google's open-sourced AX offers useful context. The pace of change is quick, and security must keep up.
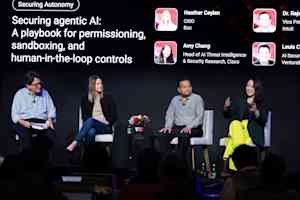
Multi-turn attacks expose the blind spot in AI red-teaming programs
Cisco's multi-turn attack study should end the illusion that single-shot red teaming tells you anything about your AI agents. When 15 flagship models were hit with 6,986 adaptive, conversational attacks, attackers broke through 88.3% of the time. That's not an edge case. It's the default. Single-turn testing didn't just miss the risk; it ranked models in a completely different order than multi-turn testing did. If you're still testing agents like they're static code, you're not testing at all.
Your AI agents have real access. Their security controls don't.
The majority of enterprises are already feeling the agent security gap, 54% have faced an incident or near-miss. Yet most are still securing autonomous agents with shared credentials and borrowed provider guardrails, leaving identity and isolation controls behind. The gap is clear: agents are proliferating faster than the controls needed to contain them. Explore how your defenses measure up and discover where the structural weaknesses actually live.
AI agents are outpacing the security designed to contain them
Most enterprises are already feeling the agent security gap, 54% have hit an incident or near-miss, yet most agents still share credentials. The controls that would contain them, like scoped identity and sandboxing, lag furthest behind. The result is a stack borrowed from providers, comfortable to use but thin on containment. The data is clear: adoption is running ahead of the controls meant to hold it. It's time to close that distance before the next near-miss becomes the incident.