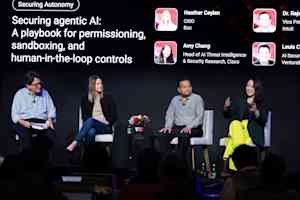
The security industry has spent years selling a comforting fiction: that a single well-crafted prompt can reveal whether an AI system is safe. Cisco's data dismantles that illusion with brutal efficiency. When Amy Chang's team ran 6,986 multi-turn attacks against 15 flagship models, the results were not a marginal difference between testing methods. Attackers who adapted their approach across a conversation broke through as often as 88.3% of the time, and every single model tested showed non-trivial exposure. The two testing styles did not even rank the models in the same order of vulnerability. That last detail is the one that should keep you up at night. It means single-turn red teaming is not just incomplete; it is actively misleading, giving security teams a false sense of confidence while the real attack surface behaves entirely differently.
The gap between what enterprises are doing and what the threat demands is stark. VentureBeat's own Pulse survey found that 54% of enterprises have already experienced a confirmed agent security incident or a near-miss. Yet 82% still rely on provider-native and hyperscaler controls as their primary security layer, and only 30% isolate their highest-risk agents in sandboxes. The market has noticed the mismatch, which is why Palo Alto Networks closed its $25 billion CyberArk acquisition and CrowdStrike paid $740 million for SGNL, all aimed at the identity and isolation layer most organizations have not finished building. But the deeper problem is not a lack of tools. It is a lack of realism about how attackers actually operate. As Chang put it, multi-turn attacks are "more realistic of how we are actually engaging with our models," and that realism is exactly what most testing programs lack.
The panel's most useful insight, however, was not the attack data. It was the defensive answer, which turned out to be refreshingly unglamorous. Chang's starting point is not a new AI-powered security product. It is Cisco's Integrated AI Security and Safety Framework, which stipulates how AI can be compromised across the entire lifecycle, from modality through supply chain. From there, teams work backward from real incidents, trace how each attack was achieved, and build strategy around coverage and mitigations. Box's Heather Ceylan echoed the same theme with a story about her own SOC agents. Box deployed agents with human approval required for every action, trust built quickly, and then the agent made one mistake. All the accumulated trust vanished, and the team had to start over. Her conclusion was blunt: "The days of secure code reviews where a human's looking at the code and those are done." The future belongs to teams that treat security as a continuous, multi-turn process, not a one-time gate.
If you take one thing from this story, make it this: test the way attackers attack, across full conversations, continuously, or find out in production what your single-turn red teaming missed. The specific number to watch is not 88.3%, though that should alarm you. It is the 59% of enterprises shopping for agent security tooling over the next 12 months. Those buyers will be bombarded with point solutions, but the panel's answer is more fundamental. It comes down to least privilege access, ephemeral sandboxes, and deterministic tool-call restrictions. Intuit's Rajesh Parekh built an entire platform, GenOS, to abstract security and risk so individual agent developers never reinvent protection. For the rest of us, the question is simpler: will you treat security as a snapshot or a conversation? The models are already having that conversation with attackers. It is time your defenses did too.