bugs
5 stories filed under bugs on Beyond Market Intelligence. The newest of them: “How Silent Tensor Broadcasting Creates Hidden Model Errors”, “OpenAI restricts cyber program access, challenging trusted researcher partnerships”, and “Reproducible research needs more than promises: it needs code.”. Silent broadcasting can quietly corrupt your model's performance, often without a single error message to guide you. OpenAI has revoked researchers' access to its Trusted Access for Cyber program, a move that raises questions about how the lab balances security research with practical safeguards. Acme AI is the next-generation, AI-powered spreadsheet platform built to replace Excel and redefine how analysts, data scientists, and enterprise teams work… The list below is every bugs story on Beyond Market Intelligence, newest first.
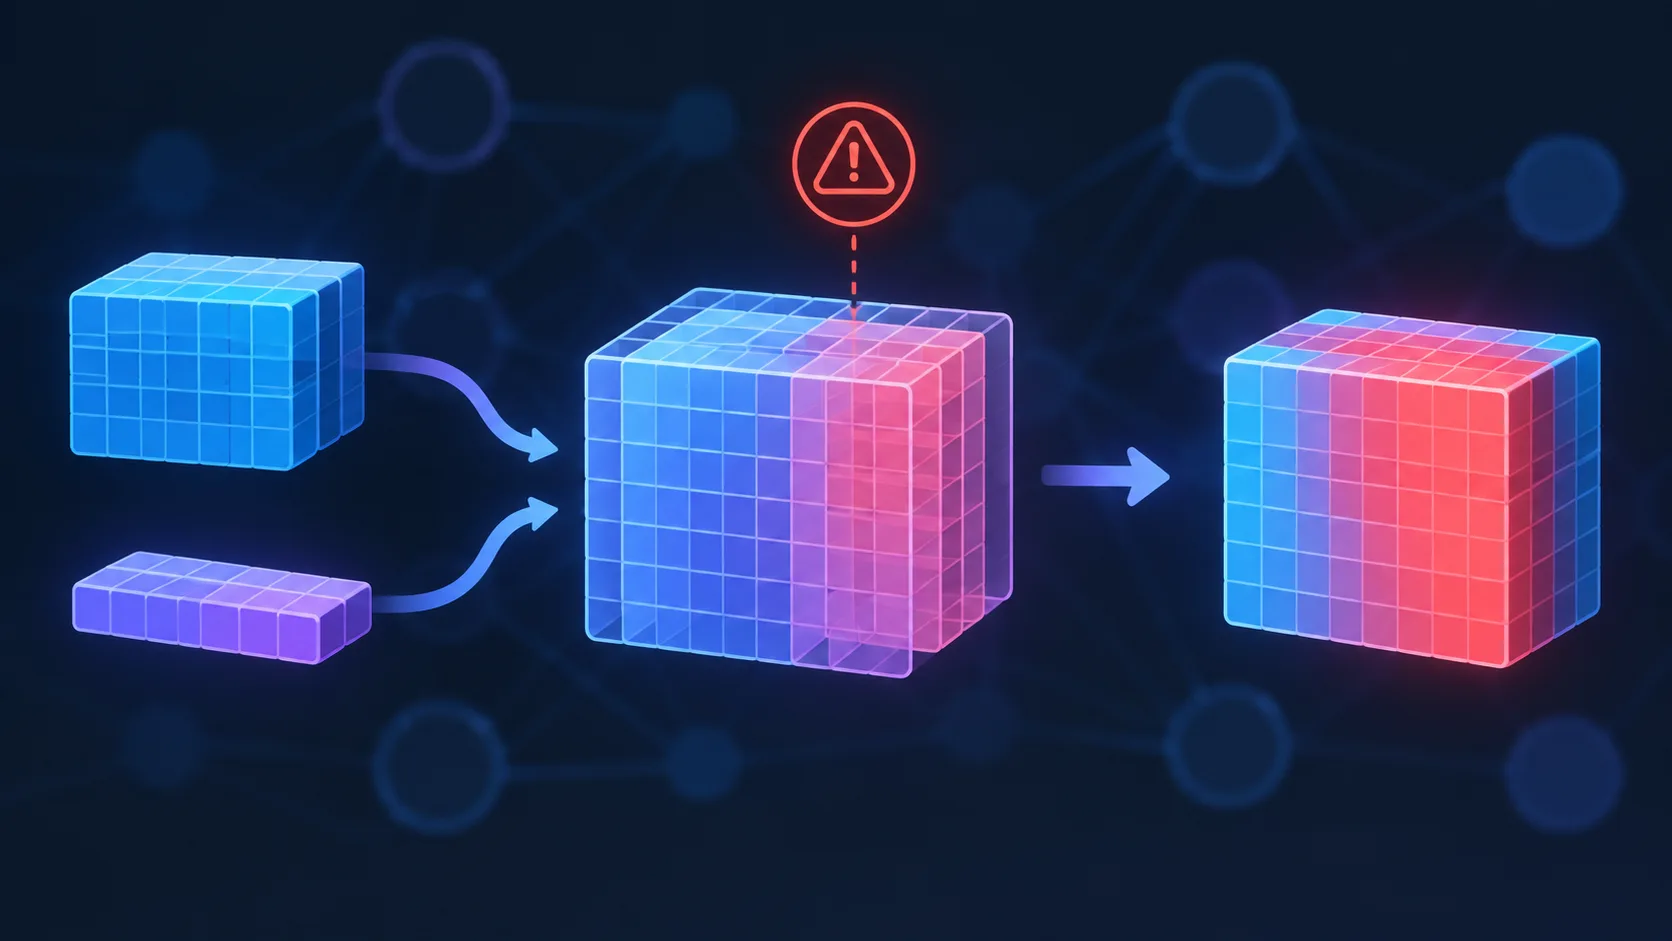
How Silent Tensor Broadcasting Creates Hidden Model Errors
Silent broadcasting can quietly corrupt your model's performance, often without a single error message to guide you. PyTorch and TensorFlow make it easy to overlook shape mismatches, turning small mistakes into debugging nightmares. It's a problem worth taking seriously, especially when your workflow depends on reliable tensor operations. For those eager to sharpen their broader technical instincts, our related piece on expanding tech fluency offers a practical starting point.

OpenAI restricts cyber program access, challenging trusted researcher partnerships
OpenAI has revoked researchers' access to its Trusted Access for Cyber program, a move that raises questions about how the lab balances security research with practical safeguards. The program's premise is sound: give capable defenders better models so they can report vulnerabilities faster, closing gaps before they're exploited. But cutting off access, even selectively, risks chilling the very collaboration that accelerates fixes. If the goal is safer AI, transparency about these decisions matters as much as the tools themselves.
Reproducible research needs more than promises: it needs code.
Twelve papers reviewed this year, and only one came with full code. That's not a fluke; it's a pattern. One reviewer's experience mirrors a systemic incentive problem: hiding code costs nothing, while sharing it invites scrutiny that can sink a paper. We should be demanding reproduction-ready submissions, not treating them as optional. If we want quality and reproducibility, we need real penalties for non-compliance.

AI tools help Google patch more Chrome bugs in a single month
Google says AI helped it fix more Chrome bugs in June than in the prior two years combined. That is a striking signal, not just about volume, but about how quickly large language models are reshaping the mundane work of security. For two years, experts have warned this day was coming. It is here. The shift is practical, not theoretical. If you are curious how AI is changing the tools you rely on daily, this is worth exploring.

Build Your Own LLM Runtime with a Guided Tour of Real Bugs
There's a particular satisfaction in packing your own weights and capturing your own CUDA graphs, and that's exactly the terrain this walkthrough covers. The post traces the building of annotated-llm-runtime on an H100, with three bugs generating most of the hard-won annotations. It's a practical, grounded tour for anyone curious about the mechanics beneath the abstraction. For broader context on the distributed side, *Unlock LLM Training* pairs well here, though this piece stands firmly on its own.