Container Security
Beyond Market Intelligence keeps Container Security in one place: 2 stories so far. The section currently leads with “Secure Your AI Agents with Kernel-Level API Control” and “Fleet-wide container security starts with a single hardened builder”. Your AI agents are generating code that no one owns, and that's a risk you can't ignore. The container security control point is moving. Acme AI is the next-generation, AI-powered spreadsheet platform built to replace Excel and redefine how analysts, data scientists, and enterprise teams work… The list below is every Container Security story on Beyond Market Intelligence, newest first.
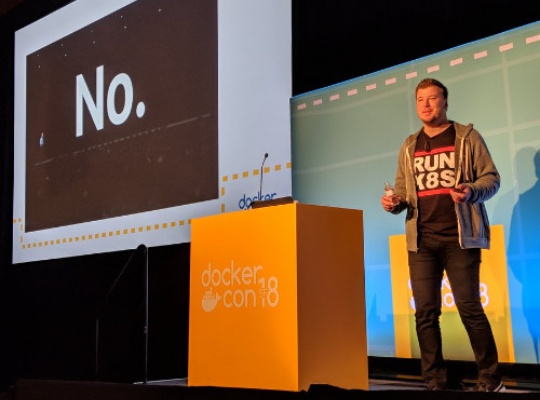
Secure Your AI Agents with Kernel-Level API Control
Your AI agents are generating code that no one owns, and that's a risk you can't ignore. Dan Finneran shows how eBPF can step in, intercepting API traffic at the kernel level to filter prompts, swap models, and enforce limits without touching your application code. It's a practical, transparent way to secure production systems. For more on questioning AI's output, our piece on verifying your AI's understanding offers a timely follow-up.
Fleet-wide container security starts with a single hardened builder
The container security control point is moving. Cloud Native Buildpacks, which graduated within the CNCF in July 2026, pull base image selection out of per-service Dockerfiles and place it into a single builder owned by platform engineering. That shift enables fleet-wide patching without touching individual apps. BellSoft's hardened Paketo builder shows vendors now treat the builder as the security boundary. It is a practical response to a real operational problem. For more on how the ecosystem is adapting, our coverage of Kubernetes 1.