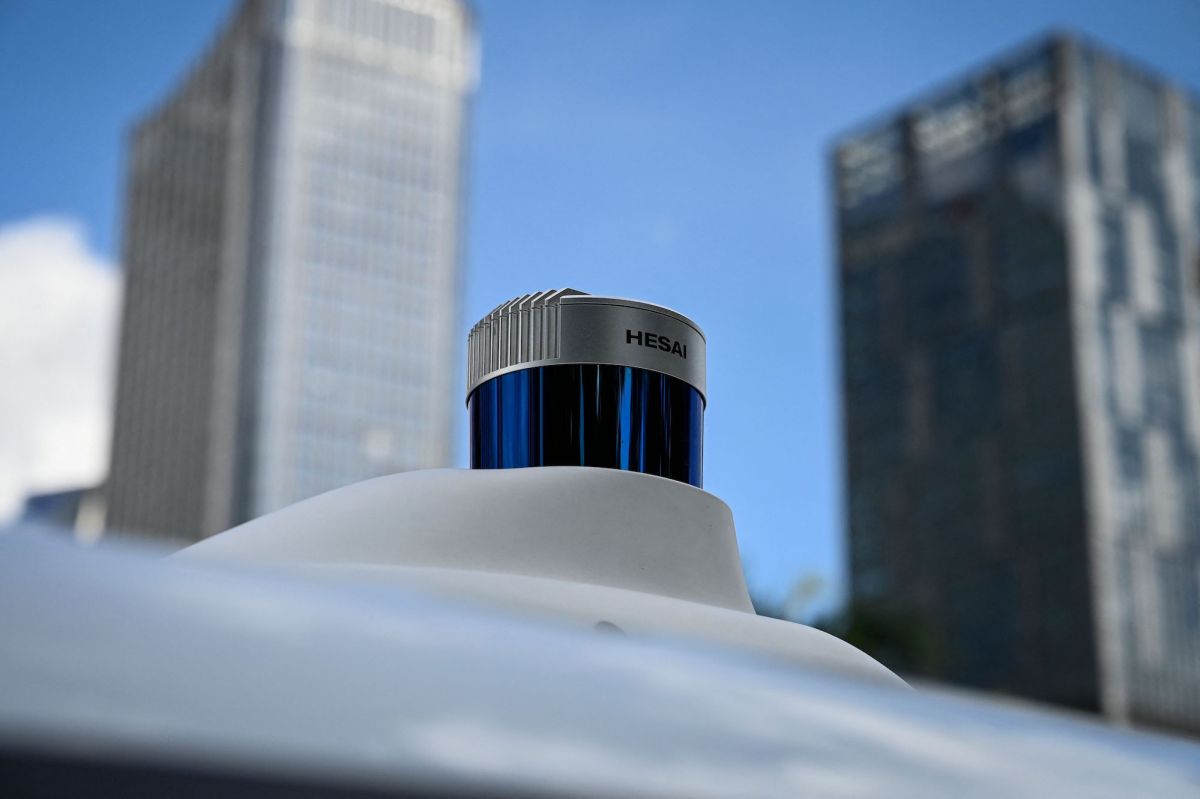
The Idaho National Laboratory is probing Chinese lidar systems for security vulnerabilities, and the research is backed by a consortium from the electric and autonomous vehicle industries. That funding detail matters. It suggests the companies that would deploy these sensors at scale are not waiting for a mandate. They are paying for answers now, because the cost of discovering a flaw after deployment is far higher than the price of the investigation itself.
This is a practical move, not a political one. Lidar is the sensing backbone for autonomous driving, and if a sensor can be remotely manipulated or tricked into misreading its environment, the consequences are not theoretical. A vehicle that cannot trust its own perception is a liability. So when an industry group funds a national lab to stress-test Chinese hardware, they are doing exactly what mature engineering organizations should do: they are treating security as a supply chain property, not an afterthought. This connects to a broader pattern we are tracking across the AI-native infrastructure space. When Anthropic Explores Akamai's Cloud for AI-Native Workloads, the question is not whether the compute is fast, but whether the architecture can be trusted under pressure. Similarly, when Nscale Secures $3.36B to Advance AI-Native Spreadsheet Infrastructure, the funding is meaningless if the underlying data pipelines are compromised. Security reviews are becoming the gatekeeper for adoption, whether we are talking about cloud contracts or sensor stacks.
What stands out here is the quiet acknowledgment that hardware trust is not binary. The review is not about banning Chinese lidar outright. It is about understanding exactly what these sensors do, how they handle data, and whether they can be coerced into lying. That is a mature posture, and it is one more businesses should adopt for their own critical infrastructure. The same logic applies to the recent wave of crypto thefts, such as the one linked to North Korean hackers that drained $351 million from Bitget. In that case, the vulnerability was not in the blockchain itself but in the tools and interfaces people trusted. The lesson is consistent: trust must be verified, not assumed.
For our readers, the takeaway is direct. If you are integrating third-party hardware or software into your workflow, ask who is testing it and who is paying for that testing. The fact that an industry consortium is funding this research tells you they expect to keep using these sensors, but with their eyes open. That is the standard to hold your own vendors to. The open question worth watching is whether the findings from this review will be shared publicly or kept internal. If the results stay private, the protection is limited to the consortium members. If they are published, the entire industry gets smarter overnight. That distinction will tell you whether this is about collective security or competitive advantage. We would tell any reader building on autonomous vehicle technology to follow that detail closely, because it will define how much of this knowledge becomes a public good.